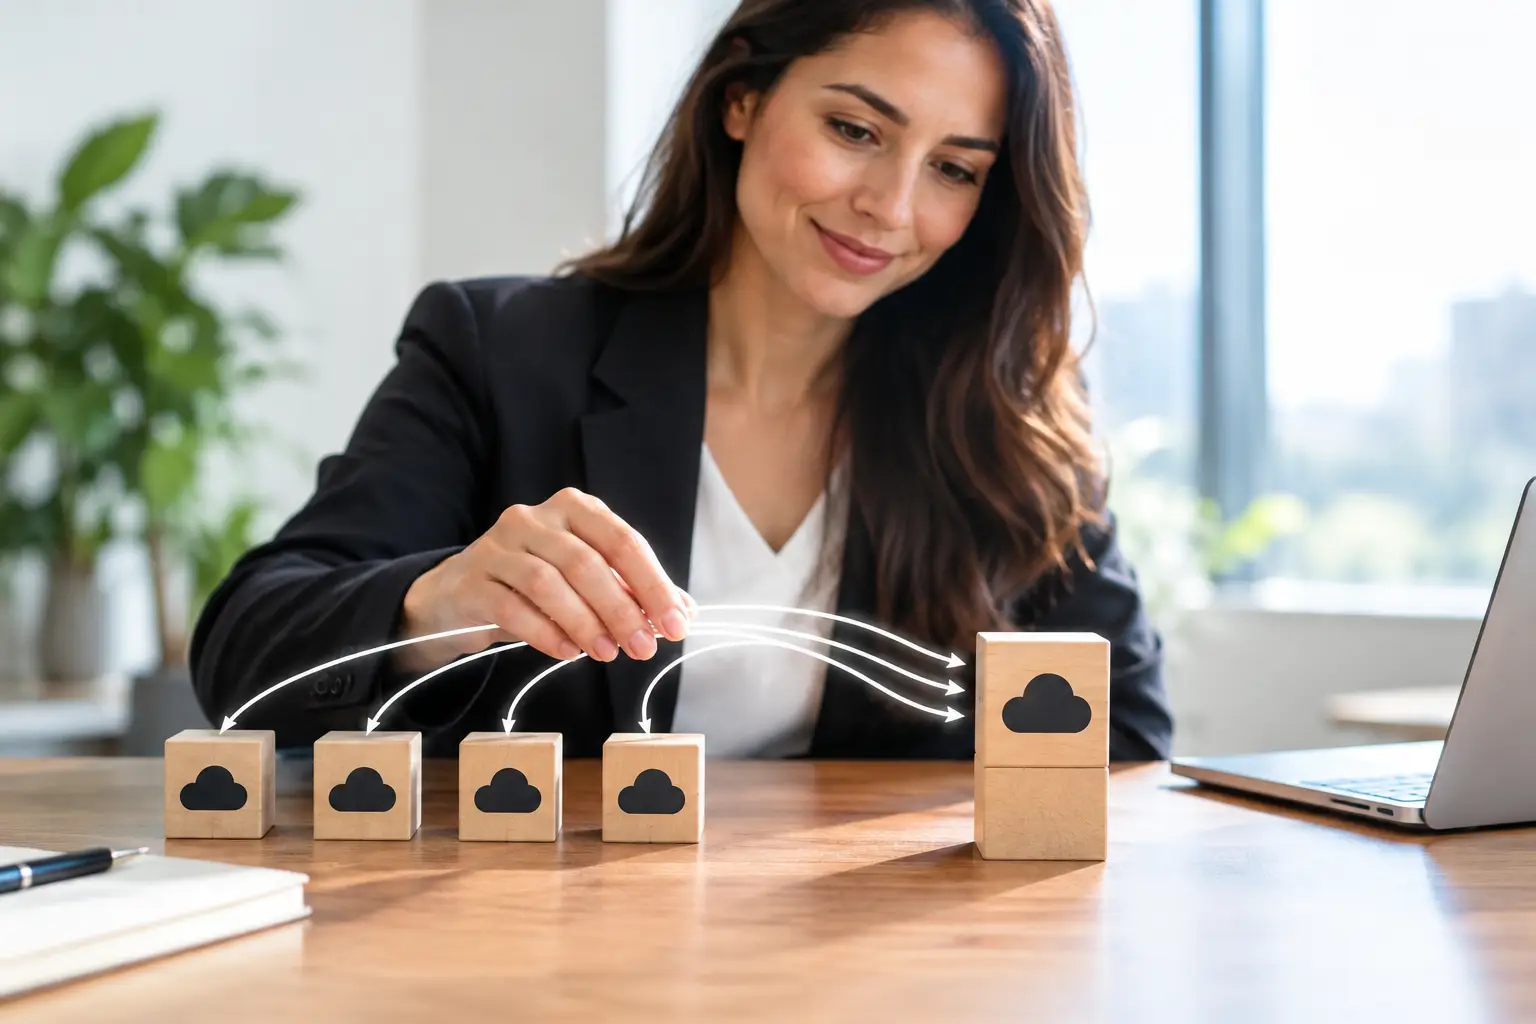
A growing business can accumulate technology vendors the way it accumulates software subscriptions: gradually, quietly, and without a clear operating plan. One provider manages email, another handles backups, a third sells security tools, and an outside consultant is called when something breaks. IT vendor consolidation changes that model. Done well, it does not simply reduce the number of invoices. It creates clearer accountability, stronger security oversight, and a technology operation built to support growth.
For organizations with 50 to 200 employees, fragmented vendor relationships often become a hidden drag on performance. The cost is not limited to duplicated tools or inconsistent support. It appears in slow incident response, unclear compliance evidence, missed handoffs, executive frustration, and difficulty proving maturity to a major client, insurer, auditor, or partner.
Cybersecurity is not just protection. It is positioning. Consolidation gives leadership a more credible way to demonstrate that technology, risk, and business continuity are managed as one operating priority.
Why IT Vendor Consolidation Matters to Executives
When multiple vendors share responsibility for the same environment, accountability can become diluted. If an employee clicks a malicious email link, for example, the email provider may point to endpoint security, the endpoint provider may point to user training, and the backup provider may explain that recovery is outside its scope. Each answer may be technically reasonable. None gives the CEO confidence that someone owns the business outcome.
A consolidated model establishes a clearer chain of responsibility across the technology environment. That includes identity and access controls, endpoints, email security, network protection, backup and disaster recovery, monitoring, compliance documentation, and user awareness. It also gives leadership a more complete view of risk, priorities, and investment decisions.
This matters most when the business faces a consequential moment: onboarding with an enterprise client, responding to a security questionnaire, renewing cyber insurance, opening a new location, supporting remote teams, or recovering from an operational disruption. In those moments, a collection of disconnected vendors is not a strategy. It is a coordination problem.
Consolidation Is Not the Same as Putting Everything With One Provider
The goal of IT vendor consolidation is not blind centralization. A business may still need specialized legal counsel, industry-specific software, telecommunications partners, or niche compliance expertise. The question is whether those providers fit into a coordinated security and operating model.
The right model depends on the organization. A healthcare practice handling patient information may need an integrated approach to HIPAA-aligned safeguards, continuity planning, mobile access, and audit evidence. A construction firm may prioritize job-site connectivity, secure bid and project data, executive mobile protection, and controls against wire fraud. A financial or professional-services firm may need tighter governance over personal information, privileged access, retention, and client security requirements.
Consolidation should therefore focus on the systems that create shared risk and require shared visibility. Security tools, managed IT, monitoring, backup, identity, compliance reporting, and strategic planning are usually stronger when governed together. Specialized business applications can remain separate, provided their security, access, recovery, and vendor obligations are understood.
The Business Case Extends Beyond Cost Reduction
Savings can be a welcome result of reducing overlapping licenses and administrative work. But cost reduction alone is an incomplete case for consolidation. The larger value is operational maturity.
A consolidated technology partner can connect what happens at the help desk with what appears on an executive risk report. It can identify whether a recurring support issue points to a training gap, an aging device fleet, a weak access policy, or a business process that needs redesign. That connection turns IT from a series of isolated service tickets into a management discipline.
The resulting benefits are tangible:
- Faster decision-making because leadership has a single, accountable view of technology priorities.
- More consistent protection because controls are designed to work together instead of operating in silos.
- Stronger audit and questionnaire readiness because evidence, policies, and remediation activities are organized.
- Better business continuity because backup, recovery, communications, and operational dependencies are planned as a whole.
- Greater client confidence because the organization can explain how it manages sensitive data and operational risk.
Trust opens markets. Organizations that can demonstrate disciplined security and continuity practices are better positioned for larger contracts, regulated opportunities, and enterprise onboarding.
Where Fragmented Vendors Create the Most Risk
The most serious gaps tend to appear at the boundaries between vendors. Identity is a common example. If one provider manages Microsoft 365, another handles endpoint security, and a third oversees network access, who verifies that departed employees lose access everywhere? Who investigates unusual sign-in activity? Who confirms that multifactor authentication policies are enforced consistently?
Backup and recovery present another concern. A backup vendor may confirm that data is being copied, but that does not necessarily mean the organization can restore a critical application within the timeframe the business needs. Recovery objectives must align with actual operations, including line-of-business systems, cloud data, shared files, configurations, and communications.
Compliance can become equally fragmented. A policy document, a vulnerability report, a user-training record, and an incident-response plan do not create readiness if they are outdated, disconnected, or unsupported by daily operations. Compliance maturity requires evidence that controls are not merely purchased, but managed.
How to Approach IT Vendor Consolidation Without Disrupting Operations
A successful transition starts with a business-led assessment, not an immediate tool replacement. Leadership should first identify what vendors support, what data and systems they touch, what contracts and renewals exist, and where accountability is unclear. The exercise often reveals duplicated capabilities, unmanaged privileged access, and critical dependencies that were never documented.
Next, define the operating outcomes that matter. These may include a stated recovery target for key systems, continuous security monitoring, a predictable technology budget, fewer escalations between providers, or readiness for customer security reviews. Outcomes give the consolidation effort a decision framework. Without them, a company may replace several vendors yet preserve the same gaps.
The transition should be phased. High-risk items such as administrator access, endpoint visibility, email security, backup validation, and documentation deserve early attention. Other services can move according to contract dates, business calendars, and the organization’s tolerance for change. For a medical practice, avoiding disruption to patient care may shape the schedule. For a contractor, the timing may need to account for active project milestones and field operations.
Finally, establish executive governance. A consolidated provider should offer regular reviews that translate technical findings into business decisions: which risks deserve investment, where compliance evidence is incomplete, how technology supports expansion plans, and what continuity assumptions need testing. If the reporting does not help leaders make decisions, it is not strategic enough.
What a Strategic Partner Should Be Able to Own
A capable managed IT and cybersecurity partner does more than respond to support requests. It brings together prevention, detection, response, recovery, and governance under a coordinated model. This includes maintaining visibility across users, devices, identities, email, networks, cloud services, and critical data.
At CMIT Solutions of LA, CyberSuite 1.9.4.26 is designed around this principle. Its integrated approach brings Zero Trust architecture, continuous protection, compliance alignment, executive mobile risk intelligence, and strategic oversight into one operating model. The objective is not to create a larger stack of tools. It is to make protection measurable, management accountable, and growth less constrained by technology uncertainty.
For executive teams, the test is straightforward: can your providers explain who owns your most material technology risks, how recovery will work, what evidence supports your compliance posture, and what investments will strengthen your market position? If the answer requires several meetings and competing explanations, the vendor model may be holding the organization back.
Protection is the baseline. Growth is the objective. A focused IT vendor consolidation assessment can give your leadership team the clarity to reduce friction, build trust, and move into larger opportunities with greater confidence.