A finance director approves invoices from home. A project manager accesses plans from a job site. A physician reviews sensitive records on a mobile device. In each case, Zero Trust vs perimeter security is not an abstract technology debate. It is a decision about how confidently an organization can protect operations, prove maturity, and keep moving when work happens beyond a single office network.
For years, perimeter security was the sensible default. Build a protected network boundary, place critical systems inside it, and treat traffic outside that boundary with greater suspicion. That model still has value. Firewalls, secure network configurations, and monitored gateways remain foundational controls.
The business environment has changed, however. Cloud applications, remote access, mobile devices, outsourced partners, and distributed teams have dissolved the idea that a company has one clear edge. A perimeter alone can no longer carry the full burden of trust.
Zero Trust vs Perimeter Security: The Core Difference
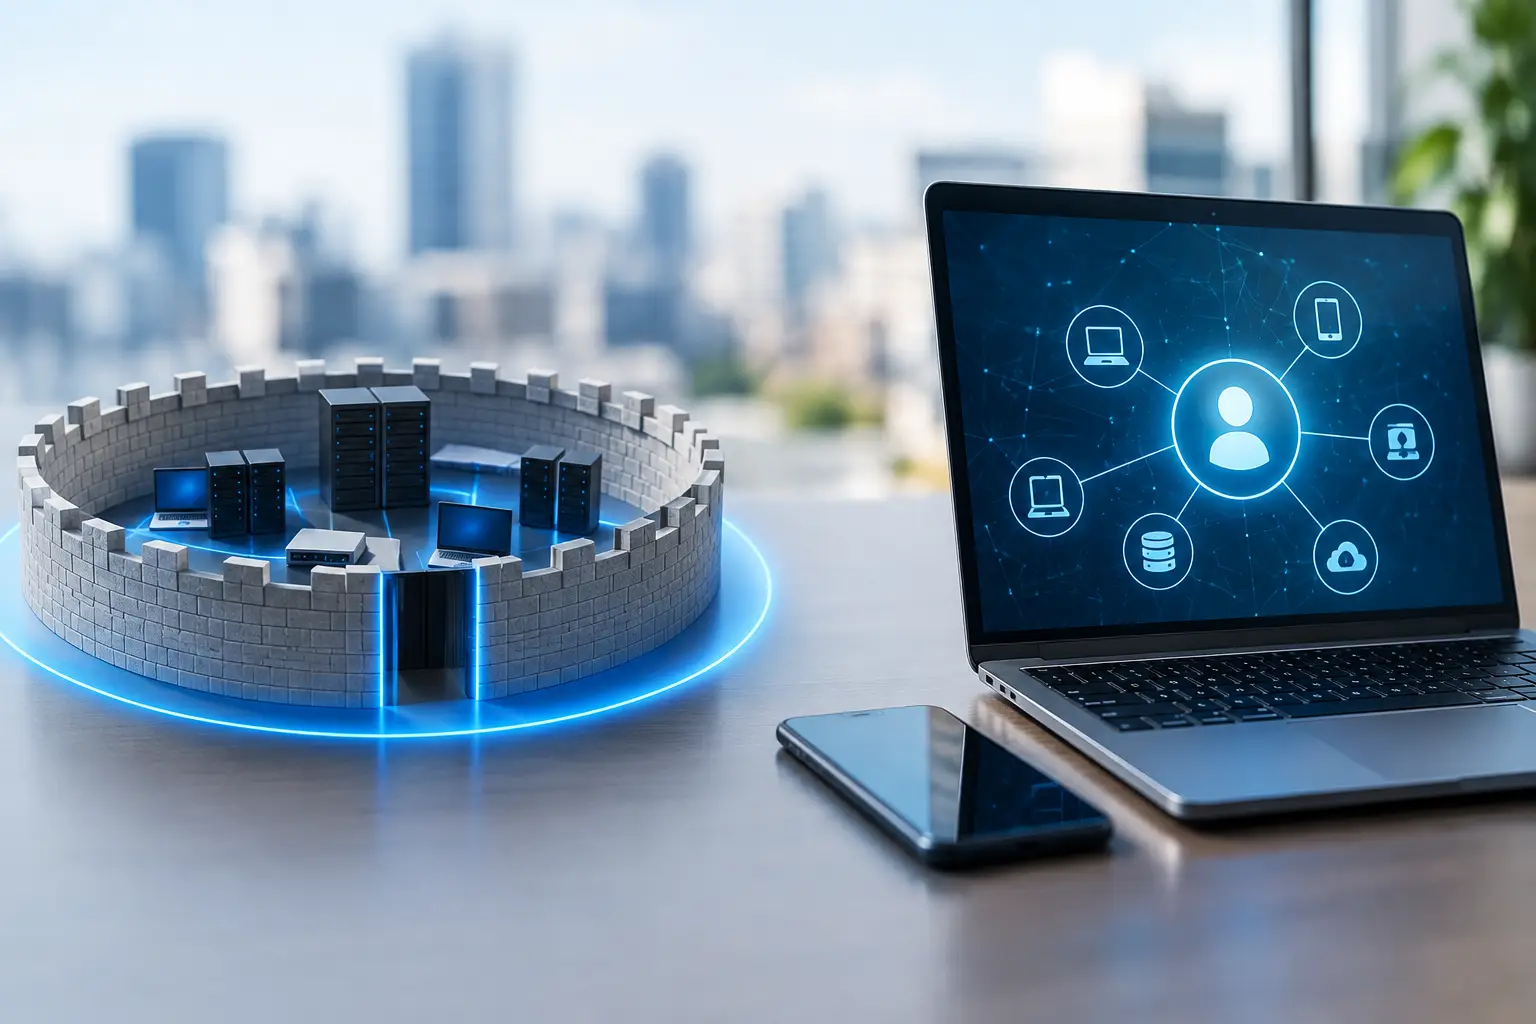
Perimeter security is built on the concept of defending the edge. If a user, device, or application is inside the protected network, it has historically received a higher level of inherent trust. Controls at the boundary inspect and limit what enters or leaves.
Zero Trust changes the starting assumption. No user, device, workload, or connection is trusted simply because it is on the company network. Access is evaluated continuously using identity, device condition, location, behavior, sensitivity of the data requested, and other relevant signals. The operating principle is straightforward: verify explicitly, grant only the access required, and assume that any credential or device could eventually be compromised.
This does not mean Zero Trust eliminates the network perimeter. It means the perimeter becomes one layer in a broader security architecture. A firewall can still block known threats and segment traffic. It simply cannot be the sole decision-maker for whether someone should access payroll, patient information, financial records, engineering files, or administrative systems.
For executives, the distinction matters because the two approaches produce different business outcomes. Perimeter-first security primarily protects a location. Zero Trust protects access to business resources wherever people, systems, and data operate.
Why the Traditional Perimeter Is Under Pressure
The perimeter model was designed for a time when most employees worked from a central office, most applications ran in a company-controlled environment, and sensitive data stayed within a relatively predictable network. Many organizations now operate across SaaS platforms, home offices, field locations, cloud infrastructure, and mobile devices.
Consider a construction firm whose superintendent needs project documents from a job site, an accounting firm serving clients through cloud platforms, or a healthcare organization that depends on secure access across clinical and administrative systems. In each case, valuable data is accessed through identities and devices that may be far from headquarters.
If a criminal obtains a valid password, a traditional perimeter may not distinguish that session from a legitimate one, particularly when the user is connecting through an approved channel. If an unmanaged or outdated device connects internally, broad network access can allow a localized issue to spread further than it should.
This is where the business cost becomes clear. The concern is not only a security incident. It is interrupted operations, delayed client work, insurance scrutiny, failed security questionnaires, reputational strain, and leadership time redirected from growth to recovery.
Cybersecurity is not just protection. It is positioning. Organizations that can demonstrate disciplined access controls and continuous oversight are better prepared to earn the confidence of enterprise clients, regulated partners, and boards.
What Zero Trust Looks Like in Practice
Zero Trust is often described as a product. In reality, it is an operating model that coordinates several controls around the question: should this specific request be allowed right now?
Identity is central. Strong multi-factor authentication reduces reliance on passwords alone, while role-based access helps ensure employees can reach the systems necessary for their responsibilities without receiving broad administrative privileges. A controller may need access to financial platforms, for example, but not to a clinical records environment or a construction project repository.
Device posture is equally important. Before granting access, the organization can assess whether the device is known, encrypted, updated, and protected by endpoint security. A device that falls below policy can be restricted or required to remediate before it reaches sensitive applications.
Segmentation limits how far an issue can travel. Rather than allowing every connected system to communicate freely, the environment is divided according to business function and risk. This approach can contain exposure and preserve continuity if one account or endpoint becomes compromised.
Continuous monitoring completes the model. Access decisions should not be static. Unusual behavior, impossible travel patterns, attempts to reach restricted information, or changes in device health can trigger additional verification or investigation.
These controls require thoughtful design. Overly rigid policies can frustrate employees and create workarounds. Overly permissive policies defeat the purpose. The right program aligns access with how people actually work, the data they handle, and the level of risk the business is prepared to accept.
The Strategic Advantages of Zero Trust
Zero Trust gives growing organizations more than a new set of security controls. It creates a more defensible and measurable approach to operational maturity.
First, it improves resilience. By limiting access and containing lateral movement, an organization reduces the chance that one compromised password or endpoint becomes an enterprise-wide disruption. Business continuity becomes more achievable when systems and data are not exposed through unnecessarily broad permissions.
Second, it supports compliance and audit readiness. Frameworks and contractual requirements vary across HIPAA, GLBA, CCPA and CPRA obligations, NIST-aligned programs, and customer security reviews. Zero Trust does not automatically satisfy every requirement, but its core practices – identity verification, least-privilege access, logging, and device governance – provide strong evidence of a disciplined control environment.
Third, it supports market access. Larger clients, carriers, and regulated partners increasingly ask how vendors protect sensitive information. An organization that can clearly explain who has access, how access is reviewed, and how suspicious activity is monitored presents a stronger answer than one relying solely on a firewall at the office.
Trust opens markets. For a business pursuing higher-value contracts or handling sensitive client data, that is not a marketing line. It is an operational reality.
When Perimeter Security Still Matters
The case for Zero Trust should not be interpreted as a case against perimeter controls. Firewalls, secure wireless configurations, DNS filtering, network monitoring, and protected remote connectivity remain necessary. They block threats before those threats reach users and systems, provide visibility into traffic, and help enforce segmentation.
The issue is whether those tools are operating as a complete strategy or as one layer within a complete strategy.
A small organization with a single location and limited cloud usage may begin by strengthening basic perimeter controls, endpoint protection, backups, and multi-factor authentication. A multi-site organization, healthcare provider, professional-services firm, or contractor with field personnel may need to prioritize identity governance, secure mobile access, and segmentation sooner.
The sequence depends on the business. The destination is the same: security controls that follow critical data and business processes rather than relying on a physical location to define trust.
Moving from Perimeter-First to Zero Trust
A successful transition is rarely a dramatic overnight replacement. It is a deliberate program that begins with visibility. Leadership should know which data is most sensitive, where it resides, who accesses it, which applications are essential to continuity, and where privileged access exists.
From there, the organization can establish stronger identity controls, enforce multi-factor authentication, review access rights, improve endpoint standards, and segment sensitive systems. Monitoring and response processes should then connect the signals from identity, devices, email, networks, and cloud applications.
This is also the point where strategy matters more than tool accumulation. Buying multiple disconnected security products may increase alerts without improving executive visibility or business resilience. A unified architecture should make accountability clear, produce usable evidence for audits and client reviews, and support employees without creating unnecessary friction.
CMIT Solutions of LA applies this approach through CyberSuite 1.9.4.26, combining Zero Trust Architecture with endpoint, network, email, mobile, compliance, and continuous monitoring capabilities under one operating model. The objective is not simply to add more controls. It is to create a security posture that supports continuity, client confidence, and scalable growth.
The Executive Question Is Not Which Model Wins
The better question is whether your current security model reflects the way your organization actually operates. If critical work now happens across cloud applications, home offices, mobile devices, partner connections, and field environments, a location-centered security strategy has a structural limitation.
Perimeter security remains necessary. Zero Trust adds the discipline needed to manage access in a distributed business. Protection is the baseline. Growth is the objective.
The next productive step is to assess where trust is currently assumed, where access is broader than necessary, and which business processes would be most affected by a compromised identity or unmanaged device. Those answers create a practical path toward stronger resilience and a more credible position in the markets you intend to serve.